

Still Skipping MFA?
You followed the rules. Strong password. Maybe even a unique one. But without MFA, it’s still just one unlocked door.
A password (even a good one) isn’t enough. Without MFA, you’re just one breach away from total access. In this post we explore why multi-factor authentication (MFA) is no longer optional, why so many organizations still resist using it everywhere, and how attackers are bypassing weak implementations to steal identities and infiltrate systems – one unprotected account at a time.
MFA is NOT Optional!
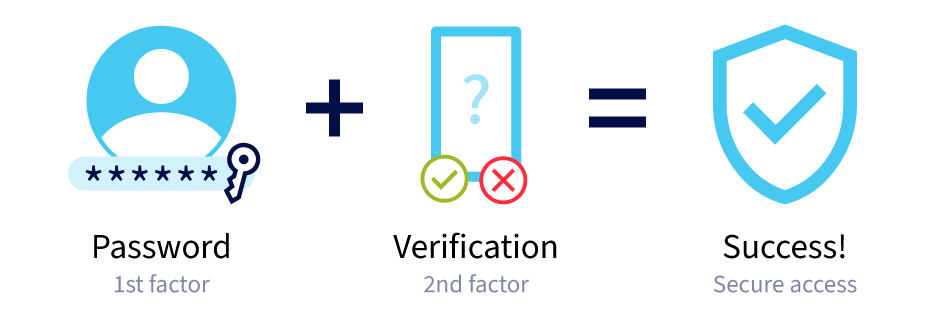
What is MFA – and Why It Works
Multi-Factor Authentication (MFA) protects your accounts by requiring more than just a password. It combines two or more types of verification:
- Something you know: Your password
- Something you have: A phone, security key, or authenticator app
- Something you are: Biometrics like fingerprint or face recognition
This layered approach drastically reduces the risk of compromise—even if your password is stolen. That’s why MFA stops most attacks cold, especially phishing and credential stuffing attempts. If you’re not using it, you’re one exposed login away from disaster.
Why So Many Still Resist MFA
NOT using MFA is not only unwise – it’s insane! A simple (poor) choice that daily robs individuals and organizations of potentially EVERYTHING. So what’s your excuse?
- “It’s annoying.” “It slows me down.” “I lose my phone/not always available.”
- “I don’t know how to set it up” – many small business leaders or individuals assume MFA requires technical complexity or expensive tools.
- “We’ll roll it out later” – MFA is seen as a “nice-to-have,” postponed until after a breach or compliance deadline forces the issue.
- “Too many apps, too much confusion” – people get overwhelmed trying to manage multiple MFA apps and account settings across platforms.
- “It’s just me, it’s not like I’m a target” – individual users underestimate their risk and delay adoption because they assume attackers go after larger fish.
WARNING!
Missing MFA Disasters - Are You next?
Time and time again, devastating breaches could’ve been stopped cold by one simple layer of security: MFA. From billion-dollar ransomware attacks to insider leaks and stolen emails, the stories keep piling up—because someone, somewhere, skipped that second factor. Here is (a very short list) of real-world breaches that could have been completely prevented with basic MFA in place.
- The ITRC 2024 Data Breach Report says 94% of breached organizations could’ve avoided the attack if MFA had been in place. (CyberWyoming)
- In 2024, four out of six mega‑breaches (Ticketmaster, AT&T, Change Healthcare included) used credential‑based attacks where MFA was missing on critical accounts. (CyberWyoming)
- Microsoft states that over 99.9% of automated account‑compromise attacks can be halted by turning on MFA. (Microsoft)
PRO TIP: All MFA Is Not Created Equal
Some stop hackers in their tracks—others just look secure. Here’s how to spot the difference.
Strong MFA
- App-based authenticator codes (e.g. Google Authenticator, Duo, MS Authenticator)
- Biometric authentication (fingerprint, face ID)
- Hardware security keys (Yubikey, Titan Key)
- Push notifications with location/context
- Separate-device MFA methods (e.g., phone + laptop)
Week/Poor MFA Practices
- SMS-based codes (can be intercepted)
- Email-based MFA (easily phished)
- Using the same device for MFA + login
- Approving push requests without checking
- One-tap approvals that are easy to spoof
What “Good MFA” Looks Like
Here are practices that differentiate “MFA theater” from “MFA security you can rely on:”
- Not enabling SMS codes – but using authenticator apps, push notifications, or even hardware keys
- MFA Everywhere: not just high-risk and privileged access point (email, admin portals, finance) has enforced MFA
- Removing weak fallback options (e.g. insecure one‑time codes via SMS if better alternative exists)
- For remote access or legacy apps, layering MFA with conditions (device trust, risk‑based login) – ZTNA VPN!
How TOPCYBER21 Helps You Do MFA Right
TC21 from TechOnPurpose is a purpose built and managed “defense-in-depth” service. MFA is an intentional and integral part of the framework from start to finish.
- Out of the box: TC21 Cyber Pros work with your existing Google / Microsoft built‑in MFA; optimizing the basics to deliver optimal security for all users.
- TC21 Service & Support staff have “mandatory” MFA requirements to access all client apps and tenants – and usually include an additional ZTNA VPN requirement as well.
- Additional MFA features and upgrades are available as needed: Including MFA Push security via Keeper Enterprise, JumpCloud and Cisco Duo for greater control, and ease of use.
- TC21 bundles and add-ons can provide browser integrated MFA usage analytics, for all cloud SaaS application access – for all users.
Your MFA Next Step: Assess Adoption & Enforcement
Cybersecurity isn’t “set it and forget it.” Even with MFA in place, consistent review is essential. Tools evolve, threats shift, and users find creative ways around good policy. That’s why it’s critical to regularly assess how—and whether—MFA is actually being used across your systems. In the current context of MFA, you should do this by asking:
- Are all administrator (and executive) accounts protected by MFA?
- Does every entry point (email, cloud tools, vendor accounts, remote access) enforce MFA?
- What are our fallback methods, and are they strong enough?
- Do we log and monitor MFA‑related login failures and bypass attempts?
Coming Up: Password Reuse Was Bad. MFA Is Your Next Defense Wall.
In the next post, we’ll dig into how the all to normal/default process of giving local admin rights (Habit #3) doubles the damage when MFA is weak or absent. But first—lock down your second factor.
Ready to STOP the #CYBERInsanity?
The habits are real. The risks are rising. And doing nothing? That’s not a strategy. Take the #CYBERsane next step now – while you still have a choice.
About the Author:
Matt Tankersley, CISSP is a US Navy combat veteran and the Founder & CEO of TechOnPurpose. Matt is recognized as an innovator with over 35 years of experience in Information Technology specifically in the areas of collaboration, cloud, security, and managed services. Recognizing the complexity, risk and blindsides that business owners face led Matt to create the TOPCYBER21™ Framework, which simplifies how organizations operationalize cybersecurity. Matt’s dedication to customer experience and unwavering belief that “Technology is at the Heart of Business today,” cast the foundation for our culture and simple operating philosophy: “We love what we do, who we do it with, and who we do it for.”
About TechOnPurpose:
Based in Austin, Texas, TechOnPurpose (“TOP”) delivers comprehensive managed IT and cybersecurity solutions to select clients globally. TOP’s approach to managed IT and cybersecurity continues to deliver simplified conversations and comprehensive, affordable solutions for our global customer family of Small & Medium Businesses and Non-Profits.


